What Businesses Should Know About Data Backups?
Protecting digital assets is no longer a luxury for modern organizations; it is a fundamental pillar of operational resilience. Understanding what businesses should know about data backups helps leaders move beyond simple file copying toward a comprehensive strategy that guards against catastrophic failure.
By implementing consistent, automated routines, you ensure that even in the event of a system crash or cyber attack, your core information remains accessible. This article explores the technical nuances and strategic decisions that define modern data protection, helping you build a framework that keeps your organization functional regardless of external threats or internal errors.
The Primary Purpose of Data Backups
The fundamental reason for maintaining data backups is to ensure business continuity. Without a verified copy of your information, a single hardware failure or a malicious encryption event can bring your entire operation to a standstill. You are not just saving files; you are preserving the ability to conduct business in the aftermath of a disaster.
Data loss occurs for many reasons beyond simple human error. Hardware degradation, power surges, and software corruption are common culprits that strike without warning.
When these events occur, the time taken to restore services directly correlates to the financial health of the company. A formal backup plan minimizes this downtime, turning what could be a fatal event into a manageable technical hurdle.
Many organizations fail to realize that their primary storage is not a safety net. If a server is compromised by ransomware, the primary data is encrypted, and any connected storage might be affected simultaneously.
Having an isolated, immutable backup ensures you possess a “known good” version of your records. This distinction between storage and backup is exactly what businesses should know about data backups to avoid catastrophic data loss.
Understanding the 3-2-1 Backup Rule
The industry standard for data protection is the 3-2-1 rule. It provides a clear, actionable framework that reduces the risk of total data loss to a statistically negligible level.
You should maintain at least three copies of your data. This count includes your primary working copy and two separate backups.
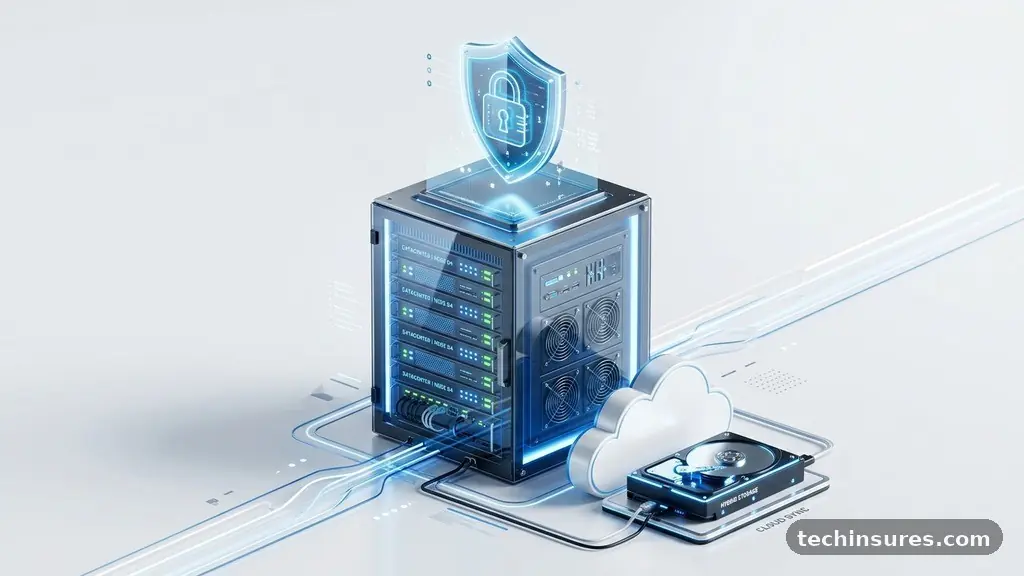
Two of those copies must be stored on different media formats. For example, one could reside on a high-speed local network-attached storage (NAS) device, while the other sits on an encrypted external drive or a tape system. Relying on a single type of hardware creates a single point of failure where a specific brand or series of drives might have a common defect.
The final “1” in the rule dictates that at least one copy must be stored off-site. This protects your organization against physical disasters like fire, flood, or theft that could destroy your office hardware. Modern cloud computing services have made this off-site requirement much easier to achieve, as data can be encrypted and transmitted to a remote data center automatically.
Choosing Between Full, Incremental, and Differential Backups
Not all backup methods serve the same purpose. A full backup captures every single file and database entry in your system.
While it is the most comprehensive, it requires significant storage space and takes a long time to complete. Most businesses perform full backups on a weekly or monthly basis to establish a baseline.
Incremental backups provide a more efficient middle ground. They only copy the data that has changed since the last backup, regardless of whether that last backup was full or incremental.
This process is extremely fast and uses very little storage capacity. However, the restore process is more complex because you must restore the last full backup followed by every subsequent incremental file.
Differential backups sit between full and incremental methods. They copy all data that has changed since the last full backup.
The primary advantage here is a faster restoration process, as you only need the last full backup and the most recent differential backup. You must weigh the storage costs against the speed of recovery when deciding which strategy best fits your business needs.
| Backup Type | Storage Space | Speed of Backup | Speed of Recovery |
|---|---|---|---|
| Full | High | Slow | Fast |
| Incremental | Low | Fast | Slow |
| Differential | Medium | Medium | Medium |
The Role of Cloud Storage in Modern Strategies
Cloud-based solutions have transformed how organizations approach data protection. By moving data to a remote facility, you remove the burden of managing physical tapes or hard drives. Many cloud providers offer automated synchronization, which ensures that your files are uploaded as soon as they are saved.
Security in the cloud relies heavily on encryption. Before data leaves your network, it should be encrypted using high-level standards like AES-256.
This ensures that even if the data is intercepted during transit or accessed by the cloud provider, the content remains unreadable. Most professional-grade services provide these features by default, simplifying the process for businesses.
Scalability is another major benefit of the cloud. As your company grows, the amount of data you generate increases exponentially.
Instead of purchasing more physical servers or storage arrays, you can simply upgrade your cloud subscription. This flexibility is a critical piece of what businesses should know about data backups in a fast-paced, digital-first economy.
Dealing with Ransomware and Cyber Threats
Ransomware remains one of the most significant threats to modern enterprises. Attackers often target backup systems specifically to prevent companies from recovering their files without paying a ransom. To combat this, you must implement “air-gapped” or immutable backups.
An air-gapped system is physically or logically disconnected from your main network. If a hacker gains administrative access to your primary systems, they cannot reach the air-gapped data to encrypt or delete it. Immutable backups, meanwhile, are stored in a format that cannot be altered or deleted for a set period, even by an administrator.
Testing your recovery process is just as important as the backup itself. Many businesses find that their backups are corrupted or incomplete only when they attempt to restore them after an attack.
You should perform regular restoration drills to confirm that your data is not just backed up, but also usable. This verification process is the only way to guarantee that your protection strategy works under pressure.
Key Components of a Successful Backup Policy
A formal policy acts as the blueprint for your data protection efforts. It should clearly define who is responsible for the backups and how frequently they should occur. Without documentation, backup procedures often fall by the wayside as staff turnover occurs or priorities shift.
Your policy should also categorize data by importance. Not every file is mission-critical.
You might prioritize financial records and customer databases for hourly backups, while less sensitive internal documents are backed up daily. This tiered approach optimizes your storage budget and ensures that the most vital information is protected most frequently.
* Define clear roles and responsibilities for IT staff.
* Establish a schedule for automated daily or hourly backups.
* Perform monthly restoration tests to verify file integrity.
* Maintain an off-site copy of sensitive data.
* Keep detailed logs of every backup and restoration attempt.
* Review the policy annually to account for new software or hardware.
By documenting these requirements, you ensure that every member of the team understands what is expected. Consistency is the primary factor in effective data protection, and a written policy provides the structure needed to maintain that consistency over time.
Integrating Backups with Business Continuity Planning
Data backups are only one part of a larger business continuity plan. You must also consider how your team will function if the main office is inaccessible or if your primary software platform goes offline. A backup of your data is useless if you have no hardware to load it onto or no internet connection to access the cloud.
Consider the “Recovery Time Objective” (RTO) and “Recovery Point Objective” (RPO). The RTO is the maximum time you can afford to be down before your business suffers significant damage.
The RPO defines how much data loss you can tolerate, measured in time. For example, if you back up every 24 hours, your RPO is 24 hours.
Aligning these objectives with your backup frequency ensures that your technical strategy matches your business goals. If you cannot afford to lose more than an hour of work, your backup schedule must run at least once an hour. Understanding this relationship is a vital part of what businesses should know about data backups to avoid misaligned expectations.
Frequently Asked Questions
How often should businesses run backups?
The frequency of your backups depends on how often your data changes and the cost of losing that information. For most active businesses, a continuous or hourly backup for critical databases is recommended, while less volatile files can be handled on a daily basis.
What is the difference between a backup and an archive?
A backup is a copy of your current, active data intended for quick recovery in the event of failure or loss. An archive is a collection of older, historical data that you keep for legal or long-term record-keeping purposes but do not need to access frequently.
Can I rely on my cloud service provider to back up my data?
Most cloud service providers offer high availability, but they do not always provide comprehensive backups of your specific files. Many providers operate on a “shared responsibility” model where they protect the infrastructure, but you are responsible for protecting the data you store within it.
Is it necessary to test my backups regularly?
Testing is the most neglected part of the backup process, yet it is arguably the most important. Without a successful test restore, you have no way of knowing if your backup files are corrupted, incomplete, or otherwise unusable.
What should I do if I suspect my backups were compromised?
If you suspect your backups were targeted by ransomware, stop all automated processes immediately and isolate the backup storage from the network. Consult with a cybersecurity professional to assess the extent of the infection and determine if a clean, offline restore point is available.
Final Thoughts
Building a reliable data protection strategy is an ongoing process that requires attention to detail and consistent maintenance. By following the 3-2-1 rule and clearly defining your recovery objectives, you create a safety net that supports long-term growth. Remember that the value of your data is not just in its creation, but in its availability when you need it most.
What businesses should know about data backups is that the effort you invest today prevents the crisis of tomorrow. Take the time to audit your current storage systems, verify your off-site copies, and perform a practice restoration this month.
Protecting your digital infrastructure remains one of the most effective ways to ensure your organization remains resilient in the face of any challenge. Start by reviewing your documentation and confirming that your team knows exactly how to trigger a recovery when the need arises.