What Is Ransomware and How Can Businesses Prepare for It?
Understanding the mechanics of modern cyber threats is essential for any leader, as learning about what is ransomware and how can businesses prepare for it serves as the foundation of a resilient digital strategy. Ransomware represents a sophisticated form of malicious software designed to block access to a computer system or files until a sum of money is paid. These attacks have evolved from simple lock screens into complex operations that exfiltrate sensitive data before encrypting it.
By implementing proactive security measures, organizations can significantly lower their risk profile and ensure operational continuity. This article explores the core components of these threats and provides actionable steps to protect your critical assets from harm.
Defining the Ransomware Threat
At its core, ransomware is a type of malware that encrypts an organization’s data, rendering it unusable until a decryption key is provided by the attacker. Once the malicious code infiltrates a network, it silently spreads to connected systems, mapping out drives and identifying high-value information. The primary objective is to hold this data hostage, forcing the victim to choose between paying a heavy extortion fee or losing access to their proprietary business information permanently.
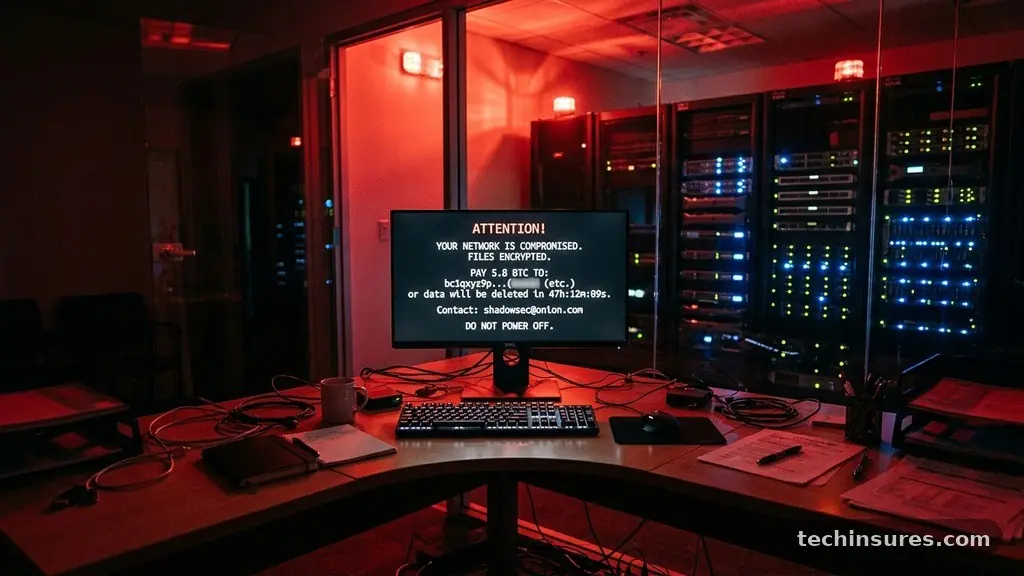
The process typically begins with a delivery mechanism, such as a phishing email containing a weaponized attachment or a drive-by download from a compromised website. Once the initial access is gained, the ransomware executes its payload, often disabling security software or deleting local shadow copies of files to prevent easy recovery. The victim is then presented with a digital ransom note, which usually demands payment in cryptocurrency, such as Bitcoin or Monero, to maintain the anonymity of the perpetrators.
Modern variants have shifted toward a strategy known as “double extortion,” where hackers steal sensitive records before triggering the encryption. Even if a business restores its systems from backups, the attackers threaten to leak the stolen data on public forums or the dark web to damage the company’s reputation. This tactic increases the pressure on the victim to pay, regardless of their technical ability to recover the encrypted files.
Common Vectors of Infection
Understanding how these attacks enter your environment is the first step in building a defense. Most incidents are not the result of a single catastrophic failure, but rather a series of small gaps that attackers exploit with precision. Email remains the most frequent entry point, as human error is often the easiest variable for criminals to manipulate through social engineering.
Another major vector involves the exploitation of unpatched vulnerabilities in internet-facing software or remote access tools. When a software developer releases a security patch, hackers scan the internet for organizations that have failed to update their systems. If a business leaves a known “door” open, it becomes a target for automated scripts that scan for these specific weaknesses.
| Vector Type | Description | Risk Level |
|---|---|---|
| Phishing | Deceptive emails tricking staff into downloading files. | High |
| RDP Exploits | Weak passwords on Remote Desktop Protocol connections. | Critical |
| Unpatched Software | Known vulnerabilities in legacy or outdated applications. | High |
| Credential Stuffing | Using stolen passwords from previous data breaches. | Medium |
Building a Strong Defensive Perimeter
Preparation requires a layered approach to security that assumes a breach might happen despite your best efforts. A single firewall or antivirus program is no longer sufficient to stop modern, targeted campaigns. Instead, you need a strategy that focuses on limiting lateral movement and ensuring that no single point of failure can bring down your entire operations.
One of the most effective strategies is the implementation of Zero Trust architecture, which requires every user and device to be authenticated before accessing resources. This prevents an attacker who has compromised one machine from easily jumping across the network to access sensitive databases. By segmenting your network into smaller, isolated zones, you trap the infection within a limited area, preventing a total system shutdown.
Endpoint detection and response (EDR) tools provide a critical layer of visibility by monitoring for suspicious behavior rather than just known file signatures. If an unknown script begins encrypting files at an unusual rate, the EDR system can automatically isolate the affected device from the network. This early intervention is often the difference between a minor incident and a company-wide crisis.
The Role of Immutable Backups
Backups are your last line of defense, but they must be designed to withstand a ransomware attack. If your backup drives are permanently connected to the network, the ransomware will likely encrypt them along with your live files. To prevent this, you should adopt the 3-2-1 rule: keep three copies of your data on two different media types, with one copy stored off-site or in an offline environment.
Immutable backups, which are files that cannot be altered or deleted for a set period, provide the ultimate safeguard. Even if a hacker gains administrative credentials, they cannot force the deletion of these records. This ensures that when the time comes to recover, you have a clean, untampered version of your data ready to be restored.
You should regularly perform “fire drills” where you attempt to restore your systems from these backups. Often, companies discover that their backup files are incomplete or corrupted only when they are in the middle of an emergency. Testing your recovery process on a quarterly basis ensures that your plan works exactly as intended when the pressure is at its highest.
Developing an Effective Incident Response Plan
An incident response plan is a living document that outlines exactly what to do when a potential breach is detected. It should include contact information for legal counsel, cybersecurity forensics experts, and insurance providers. Having this information centralized in a hard-copy format is vital, as you cannot rely on digital documents if your network is locked.
Communication is a central pillar of this plan, as you must determine who needs to be notified and when. This includes informing employees, customers, and regulatory bodies if personal data has been compromised. Transparency is essential for maintaining trust, but legal requirements vary by region, so your plan should be tailored to your local jurisdiction.
You can find more detailed guidance on creating these procedures through the official CISA StopRansomware resource center, which provides comprehensive checklists for organizations. Following these industry-standard guidelines helps ensure that your team follows a proven sequence of containment and eradication steps. By defining roles and responsibilities beforehand, you prevent the panic that often leads to mistakes during an active attack.
The Decision to Pay the Ransom
One of the most difficult dilemmas a business can face is whether to pay the ransom to retrieve their data. While paying might seem like the fastest route to recovery, it does not guarantee that the attackers will provide a working decryption key. Furthermore, paying a ransom marks your organization as a “willing payer,” which often makes you a primary target for future attacks by the same or different groups.
Security experts and law enforcement agencies generally advise against paying, as it funds further criminal activity and provides no assurance of data security. If you pay, there is no guarantee that the attackers won’t leak your data anyway, or that they won’t re-encrypt your systems a few months later. Instead of negotiating, focus your resources on rapid recovery using your verified, offline backups.
* Verify the integrity of your offline backups before initiating restoration.
* Engage with cybersecurity professionals to perform a root-cause analysis.
* Notify local law enforcement to report the incident and assist in broader investigations.
* Review and update your security posture based on the gaps identified during the breach.
Employee Training and Human Factors
Your staff members are either your biggest vulnerability or your strongest line of defense. Phishing simulations and regular security awareness training can drastically reduce the likelihood of a successful initial breach. When employees learn to identify the subtle signs of a malicious email, such as mismatched URLs or urgent, unnatural requests, they become active participants in your security ecosystem.
Create a culture where employees feel comfortable reporting suspicious activity without fear of being blamed for a mistake. If a staff member clicks a link but reports it immediately, your IT team can jump into action and stop the malware before it spreads. Silence, however, is the attacker’s best friend, as it allows them the time they need to move deeper into your systems.
Include these specific training modules in your employee onboarding:
- How to verify the sender of an email before clicking links.
- The importance of using multi-factor authentication (MFA) on all accounts.
- Procedures for reporting lost or stolen company devices immediately.
- Guidelines for avoiding the use of unauthorized software or cloud storage.
Frequently Asked Questions
What are the first steps to take if I suspect a ransomware attack?
Immediately disconnect the affected systems from the network, both wired and wireless. Do not shut down the computers, as this might destroy evidence in the volatile memory that could help with decryption. Contact your IT team or a cybersecurity incident response provider to begin the containment process.
How do I know if my backups are safe from ransomware?
Your backups are safe if they are stored in an “air-gapped” environment, meaning they have no active connection to your production network. You should also ensure they are immutable, which prevents any modification or deletion of the files for a specific retention period. Regularly testing these backups is the only way to confirm they are functional.
Is it common for businesses to pay the ransom?
While many businesses feel forced to pay, it is highly discouraged by security professionals and law enforcement. Payment does not guarantee that your files will be restored, and it often leads to the organization being targeted again. Relying on reliable, offline backups is the most secure and ethical path for long-term recovery.
What is the most effective way to prevent ransomware?
There is no single “silver bullet,” but a combination of strong multi-factor authentication, regular software patching, and offline backups is the industry standard. These measures, combined with ongoing employee training, create a multi-layered defense that is difficult for attackers to overcome.
How long does recovery typically take?
Recovery time varies based on the scale of the attack and the quality of your backups. It can range from a few hours for a small, isolated incident to several weeks for a full-scale restoration of complex enterprise systems. Having a pre-tested incident response plan significantly shortens this timeline by removing the guesswork.
Conclusion
Protecting an organization requires a dedicated commitment to vigilance and the implementation of modern security standards. By understanding what is ransomware and how can businesses prepare for it, you move from a state of reactive panic to one of organized, proactive resilience. Focus on building an environment where data is backed up securely, employees are trained to spot threats, and systems are hardened against unauthorized access.
While the threat landscape is constantly changing, the fundamentals of defense remain consistent. Prioritize the safety of your digital infrastructure today to avoid the devastating costs of a breach tomorrow. If you haven’t reviewed your security posture recently, start by auditing your backup procedures and verifying your multi-factor authentication settings across all company accounts.