Technology Risks Every Growing Business Should Understand
Navigating the digital shift requires a clear grasp of the vulnerabilities that come with scaling operations. When a company transitions from a small team to a larger enterprise, the surface area for potential failure expands significantly.
Recognizing the technology risks every growing business should understand is the first step toward building a resilient framework that protects your assets and reputation. By identifying these gaps early, leaders can make informed decisions that support sustainable growth rather than hindering it.
The Core Categories of Digital Exposure
When evaluating your firm’s exposure, it helps to classify threats into distinct buckets. Most incidents fall under cybersecurity, operational reliability, or compliance failures.
Cybersecurity remains the most immediate concern, as unauthorized access can cripple a startup overnight. Your data represents your most valuable asset, and protecting it requires more than just a standard firewall or basic antivirus software.
Operational reliability refers to the systems that keep your doors open. If your cloud infrastructure goes down or a critical software update breaks your workflow, the financial impact is immediate.
Many leaders overlook the fact that technical debt—the cost of choosing easy, fast solutions over better, long-term ones—is a major risk factor. As you scale, this debt accumulates interest in the form of system crashes, slow performance, and security holes.
Compliance and legal risks are often the most overlooked by founders. Regulations like the General Data Protection Regulation dictate how you handle user information, and ignoring these rules can lead to massive fines.
Furthermore, your employees often represent the biggest unknown variable in your risk profile. Even with the best software, a single lapse in judgment or a weak password can grant bad actors entry to your internal network.
Why Cybersecurity Threats Escalate During Growth
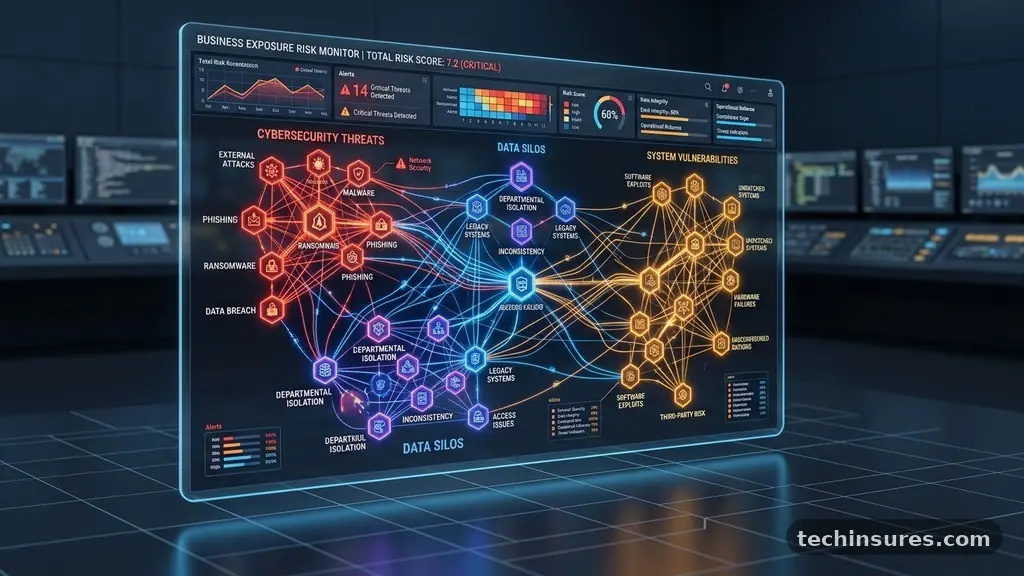
Growth often forces businesses to adopt new tools quickly, creating a fragmented digital environment. When you have multiple departments using different SaaS platforms, keeping track of who has access to what becomes a nightmare.
This complexity is exactly what attackers exploit. They look for the weak link in your chain, which is often an under-secured third-party integration or an outdated legacy application.
Phishing attacks have become increasingly sophisticated, moving beyond simple emails to include targeted social engineering. Your team members are the primary targets because they are the gatekeepers of your data.
Without proper training, employees may unknowingly grant access to sensitive systems. It is essential to treat security as a cultural requirement rather than an IT-only responsibility.
| Risk Type | Primary Impact | Mitigation Strategy |
|---|---|---|
| Phishing/Social Engineering | Data breach/Credential theft | Mandatory security awareness training |
| System Downtime | Revenue loss/Reputation damage | Redundant cloud infrastructure |
| Compliance Violation | Legal fines/Client attrition | Regular third-party audits |
| Shadow IT | Security blind spots | Centralized vendor management |
Managing Technical Debt and Infrastructure
Technical debt occurs when a team prioritizes speed to market over long-term stability. While this might be necessary in the early stages, holding onto that debt as you grow is dangerous.
Your codebase, which might have been manageable for five people, can become a liability for fifty. Regular refactoring and modernization are necessary to keep your systems from collapsing under the weight of their own complexity.
Infrastructure management also changes as you expand. Many companies start with a simple server setup, but as traffic increases, you need more sophisticated load balancing and disaster recovery plans.
Relying on a single point of failure is a common mistake that growing firms make. If your primary database resides in one location without a real-time failover, a single hardware outage could halt your entire operation.
Leadership needs to allocate a specific percentage of the development budget to maintenance. If you only spend money on new features, you are essentially ignoring the foundation of your house.
Eventually, the foundation will crack. Establishing a clear cycle for system updates ensures that your technology remains a competitive advantage rather than a source of constant frustration.
The Human Element in Risk Management
Employees are often the most significant vulnerability in any growing business. As teams expand, maintaining consistent security standards across the board becomes difficult.
A developer might leave a hardcoded password in a public repository, or a marketing manager might share a sensitive file on an unencrypted platform. These are not necessarily malicious actions, but they are high-risk behaviors.
Effective management requires a clear policy regarding digital conduct. You should limit access to sensitive systems based on the principle of least privilege.
Only those who absolutely need to access a specific database should have the credentials to do so. This limits the potential damage if a single account is compromised.
Communication is equally vital. When an employee makes a mistake, they should feel comfortable reporting it immediately rather than hiding it.
If security is treated as a punitive environment, people will bury their errors until it is too late. Encouraging transparency allows the leadership team to fix vulnerabilities before they become full-scale disasters.
Third-Party Vendor Risks
Growing companies rely heavily on external vendors for everything from payment processing to customer relationship management. Every third-party service you integrate into your stack is a potential entry point for hackers.
You are only as secure as the weakest vendor in your supply chain. It is vital to vet these companies before signing a contract.
Ask for their security certifications, such as SOC 2, and ensure their policies align with your internal requirements. Many businesses skip this step to save time, but the long-term cost of a vendor-initiated breach can be astronomical. You must also have a plan for what happens if a vendor goes out of business or suffers a catastrophic failure.
You should maintain a list of critical dependencies to manage these risks effectively:
- Cloud hosting providers and data storage services.
- Payment gateways and financial transaction processors.
- Customer support and communication platforms.
- Project management and internal collaboration software.
- Third-party APIs that feed data into your core product.
Data Governance and Regulatory Compliance
Data is the lifeblood of a growing business, but it is also a massive liability. You must know exactly what data you collect, where it is stored, and who can access it.
Many companies store information they no longer need, which increases the potential fallout in the event of a breach. Data minimization is a powerful strategy; if you do not collect it, you cannot lose it.
Compliance is not a one-time setup; it is an ongoing process. Laws evolve, and your business model will likely change as you grow into new markets.
If you expand internationally, you may fall under the jurisdiction of multiple privacy frameworks. Working with legal experts to map your data flow is essential for avoiding significant penalties and maintaining customer trust.
Focus on creating a culture of privacy by design. This means considering the security implications of a new feature while it is still in the planning phase.
It is much cheaper to build security into your product from the start than it is to bolt it on later. This proactive approach sets a professional tone that helps with enterprise-level sales and partnerships.
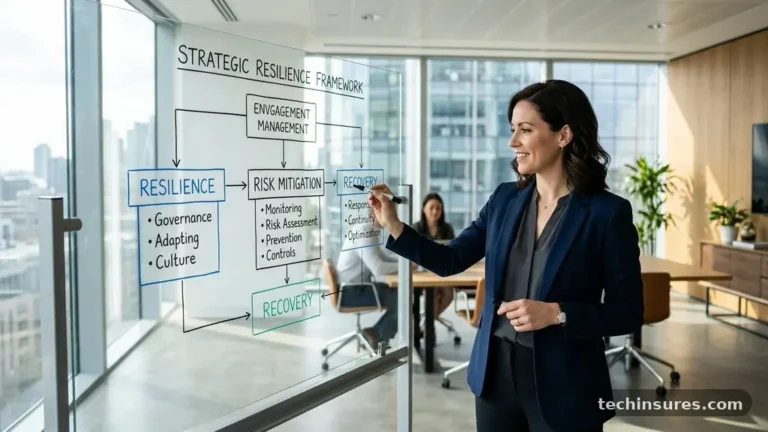
Strategic Planning for Long-Term Resilience
The technology risks every growing business should understand are not static. As your company evolves, your risk profile will change accordingly.
A startup’s biggest risk might be a lack of product-market fit, while an established company’s biggest risk is a catastrophic data breach. You need to shift your focus from rapid experimentation to risk-informed decision-making.
Leadership teams should conduct regular risk assessments to identify emerging threats. This is not just a job for the IT department; it requires input from finance, operations, and HR.
By bringing different perspectives to the table, you can identify blind spots that a purely technical team might miss. This holistic view is what separates resilient companies from those that struggle to recover from incidents.
Investing in insurance is another layer of protection that many growing businesses ignore until it is too late. Cyber insurance can help cover the costs of forensic investigations, legal fees, and client notification processes. While insurance is not a substitute for good security, it provides a vital safety net that can keep your doors open during a recovery phase.
Frequently Asked Questions
How can I identify my most critical technology risks?
Start by performing a comprehensive audit of your digital assets and dependencies. Identify which systems would cause the most damage if they went offline or were compromised. Focus your resources on securing these high-value targets first.
What is the most common technology risk for startups?
The most common risk is often the lack of documentation and standardized processes. When a business grows quickly, undocumented workflows lead to security gaps, human error, and difficulty in scaling operations safely.
How often should we conduct security audits?
Audits should be performed at least annually, or whenever there is a significant change in your infrastructure. If you frequently add new software or move data to new cloud environments, you should consider quarterly reviews.
Is it better to build security in-house or outsource it?
Many growing businesses benefit from a hybrid approach. You should maintain internal oversight and policy management while outsourcing specialized tasks like penetration testing and 24/7 network monitoring to qualified experts.
Does cybersecurity insurance really work?
Yes, it provides financial protection for the aftermath of an attack, including legal defense and recovery costs. However, it is not a replacement for preventative measures, and insurers often require you to prove you have basic security protocols in place before providing coverage.
Building a Culture of Digital Vigilance
Understanding the technology risks every growing business should understand is a continuous journey rather than a destination. As you scale, prioritize clear communication, consistent documentation, and a culture that values security at every level of the organization. By treating digital safety as a core business function, you protect your hard-earned progress and build a foundation for long-term success.
The goal is not to eliminate risk entirely, which is impossible, but to manage it so that it never becomes an existential threat. Take the time to audit your current systems, train your team, and establish a clear plan for when things go wrong.
Your commitment to these principles today will define your company’s stability tomorrow. Reach out to your IT and security leads this week to start the conversation about your current risk posture.