How AI Is Changing the Way Businesses Manage Digital Risk
Understanding how AI is changing the way businesses manage digital risk starts with a fundamental shift in speed. Organizations no longer rely solely on manual audits or reactive security patches to protect their infrastructure. Instead, they are deploying autonomous systems that monitor vast datasets in real-time to identify anomalies before they escalate.
By integrating machine learning models, companies can now predict vulnerabilities with higher accuracy than legacy software ever allowed. This evolution represents a move toward proactive resilience, where digital risk becomes a manageable variable rather than an unpredictable threat. You will learn here how these technologies reshape decision-making, improve compliance, and safeguard assets against modern cyber threats.
Real-Time Threat Detection and Response
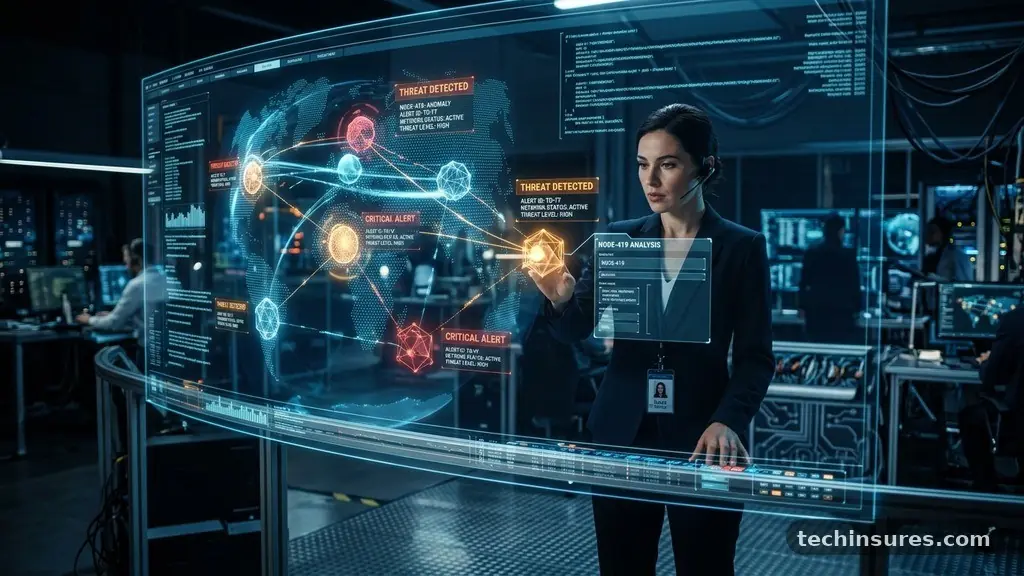
The most immediate impact of intelligence-driven security is the transition from periodic scanning to continuous observation. Traditional security operations centers often struggled with alert fatigue, as human analysts were forced to sift through thousands of logs daily.
AI platforms now automate this triage, filtering out false positives and highlighting genuine threats with remarkable precision. By processing patterns across network traffic, these tools can isolate malicious actors in milliseconds, effectively stopping an attack before it breaches the perimeter.
This capability is particularly vital for organizations handling massive volumes of data. When a system can establish a baseline of “normal” behavior, any deviation—such as an unusual login time or an unauthorized data transfer—triggers an immediate response.
This shift reduces the mean time to detect (MTTD) significantly, a metric that has historically been a major pain point for IT departments. Rather than waiting for a quarterly audit to find a hole in the armor, businesses now maintain a state of constant, automated vigilance.
Automating the Security Perimeter
Automated response mechanisms go beyond simple detection to include active remediation. When an AI identifies a compromised endpoint, it can automatically isolate that device from the rest of the network to prevent lateral movement.
This containment happens without human intervention, which is essential during late-night or weekend hours when staff availability might be limited. Such rapid action ensures that even if a breach occurs, the blast radius remains contained, protecting the broader organization from catastrophic data loss.
Enhancing Fraud Detection Accuracy
Fraud remains one of the most persistent digital risks, evolving as quickly as the tools designed to stop it. Traditional rule-based systems, which rely on static thresholds like “flag any transaction over $5,000,” are easily bypassed by sophisticated criminals.
Modern AI models, by contrast, look at thousands of variables simultaneously, including device fingerprinting, behavioral biometrics, and historical transaction patterns. This multidimensional approach makes it significantly harder for fraudulent actors to mimic legitimate behavior.
The financial sector has led this transition, often reducing false decline rates by double digits while simultaneously catching more illicit activity. For example, a system might notice that a user is typing at a different speed or navigating a site in an unusual sequence, triggering a step-up authentication request.
These micro-behaviors are nearly impossible for a bot or a human fraudster to replicate consistently. By focusing on these subtle patterns, businesses are protecting their bottom line and preserving customer trust.
The Role of Behavioral Biometrics
Behavioral biometrics represents the next frontier in identity verification. By analyzing how a person interacts with their keyboard, mouse, or touchscreen, systems build a unique profile of the user.
This creates a secondary layer of security that operates entirely in the background. If a session is hijacked, the system detects the behavioral shift immediately and blocks access, even if the attacker has obtained the correct password.
Streamlining Regulatory Compliance
Compliance is often viewed as a heavy administrative burden that pulls resources away from core business goals. However, AI is changing the way businesses manage digital risk by automating the mapping of internal controls to complex regulatory frameworks.
Instead of manually cross-referencing spreadsheets to ensure adherence to standards like GDPR or SOC2, organizations use intelligent software to monitor compliance status in real-time. This ensures that documentation is always audit-ready.
The ability to parse legal documents and regulatory updates automatically is another significant advantage. When a new law is passed or an existing regulation is updated, the software can highlight which internal policies require modification.
This removes the reliance on expensive legal consultations for every minor update. By digitizing the compliance workflow, companies minimize the risk of human error, which is often the primary cause of regulatory fines and data privacy violations.
| Risk Factor | Traditional Method | AI-Enhanced Approach |
|---|---|---|
| Threat Detection | Manual Log Review | Real-time Anomaly Mapping |
| Compliance Audit | Periodic Spreadsheet Checks | Continuous Automated Monitoring |
| Fraud Prevention | Static Rule Thresholds | Behavioral Pattern Analysis |
| Vulnerability Mgmt | Scheduled Patching | Predictive Risk Prioritization |
Predictive Risk Assessment
Traditional risk assessment is often backward-looking, relying on historical data to predict future vulnerabilities. While this has value, it fails to account for emerging threats that have no precedent.
AI models are capable of processing vast amounts of unstructured data, including global threat intelligence feeds, to anticipate where the next attack might originate. By identifying emerging trends, businesses can reinforce their defenses before a specific threat becomes a widespread reality.
This predictive capability allows for a more efficient allocation of resources. Rather than applying uniform security measures across every department, organizations can prioritize high-risk areas identified by the software.
For instance, if an AI detects an increase in phishing activity targeting specific job roles, the company can deploy targeted training or enhanced authentication for those employees immediately. This surgical approach to security minimizes disruption while maximizing protective impact.
- Continuous monitoring of dark web activity to detect leaked credentials.
- Predictive modeling of supply chain vulnerabilities to assess vendor risk.
- Automated simulation of breach scenarios to test incident response plans.
- Real-time updates to firewall rules based on global threat intelligence.
Reducing Human Error in Security
Human error remains the weakest link in any security strategy, accounting for a vast majority of successful breaches. Phishing, weak password management, and misconfigured cloud storage are constant headaches for IT managers.
AI helps bridge this gap by providing guardrails that prevent mistakes before they occur. For example, an intelligent email gateway can identify a sophisticated spear-phishing attempt that would easily fool a human, blocking the message before it reaches the inbox.
Furthermore, AI-driven configuration management tools can scan cloud environments to ensure they meet security best practices. If a developer accidentally leaves a database open to the public, the platform can automatically trigger a patch or alert the team to close the port.
This “security-by-default” approach ensures that even when employees make mistakes, the digital infrastructure remains protected. You can read more about these methodologies through the NIST Cybersecurity Framework, which outlines how to integrate these tools into existing operations.
Addressing the Challenges of AI Implementation
While the benefits are clear, implementing these tools is not without its hurdles. Organizations often struggle with data quality; if the underlying data used to train the models is biased or incomplete, the security insights will be flawed.
There is also the issue of “black box” algorithms, where the logic behind a security decision is opaque. Business leaders must demand transparency from their vendors to ensure they understand why certain alerts are being flagged.
Another significant challenge is the ongoing arms race between defenders and attackers. Cybercriminals are also using AI to generate more convincing phishing content and to automate the discovery of software vulnerabilities.
This means that businesses must continuously update their own models to stay ahead of the curve. Implementing AI is not a “set it and forget it” task; it requires a commitment to ongoing tuning, testing, and oversight by skilled professionals.
The Future of Digital Resilience
Looking ahead, the integration of AI into risk management will move toward full autonomy. We are approaching a point where systems will not only detect and contain threats but also self-heal by rewriting code or reconfiguring network segments autonomously.
This level of resilience will be essential as business operations become increasingly decentralized and reliant on interconnected cloud services. The goal is to create an environment where digital risk is mitigated at the speed of light.
This shift does not mean that human experts will become obsolete. On the contrary, the role of the security professional is evolving from a reactive analyst to a strategic architect.
Humans will be needed to set the policy, interpret the context of complex threats, and oversee the ethical implications of automated decisions. By combining human intuition with machine speed, businesses can build a defense that is not only robust but also adaptive to the complexities of the modern digital landscape.
Frequently Asked Questions
Does AI replace the need for a human security team?
No, AI does not replace human security teams. It acts as a force multiplier, automating repetitive tasks like log analysis and threat triaging so that human experts can focus on high-level strategy, incident response, and complex decision-making that requires contextual judgment.
What is the biggest risk when using AI for security?
The primary risk is the reliance on flawed data. If the AI is trained on biased or inaccurate datasets, it may produce false negatives or create security gaps. Additionally, attackers are using AI to bypass defenses, meaning organizations must maintain constant vigilance over their own security models.
How do small businesses benefit from these tools?
Small businesses benefit by gaining access to enterprise-grade security that was previously too expensive or complex to manage. Many cloud-based security platforms now offer AI-driven features as part of their standard subscription, allowing smaller firms to automate their defenses against common threats like phishing and credential theft.
Is AI-driven risk management expensive to deploy?
While there is an initial investment, the long-term costs are often lower than traditional security methods. Automating manual tasks saves thousands of labor hours, reduces the risk of costly data breaches, and prevents regulatory fines, which provides a strong return on investment for most organizations.
Conclusion
How AI is changing the way businesses manage digital risk is a narrative of empowerment and proactive defense. By shifting from manual, reactive processes to autonomous, predictive systems, companies can better safeguard their data and maintain their operational integrity. The key to success lies in viewing these technologies as partners in your security strategy rather than simple plug-and-play solutions.
To get started, evaluate your current security gaps and identify which manual processes could benefit most from automation. Whether it is improving fraud detection or streamlining compliance documentation, the focus should remain on building a flexible, intelligent architecture.
As the threat landscape continues to shift, staying ahead requires a commitment to continuous learning and adaptation. By embracing these tools, you are not just managing risk—you are building a foundation for future growth in an increasingly complex digital world.