Cyber Insurance Explained: What Does It Actually Cover?
Getting a handle on cyber insurance explained: what does it actually cover is a vital step for any modern business facing digital threats. While many assume these policies are purely for large corporations, the reality is that organizations of all sizes now rely on this protection to survive significant data breaches.
By understanding the nuances of these agreements, you can better protect your assets and maintain continuity when a security incident occurs. This article breaks down the core components of these policies, providing the clarity needed to make informed decisions about your digital risk management strategy.
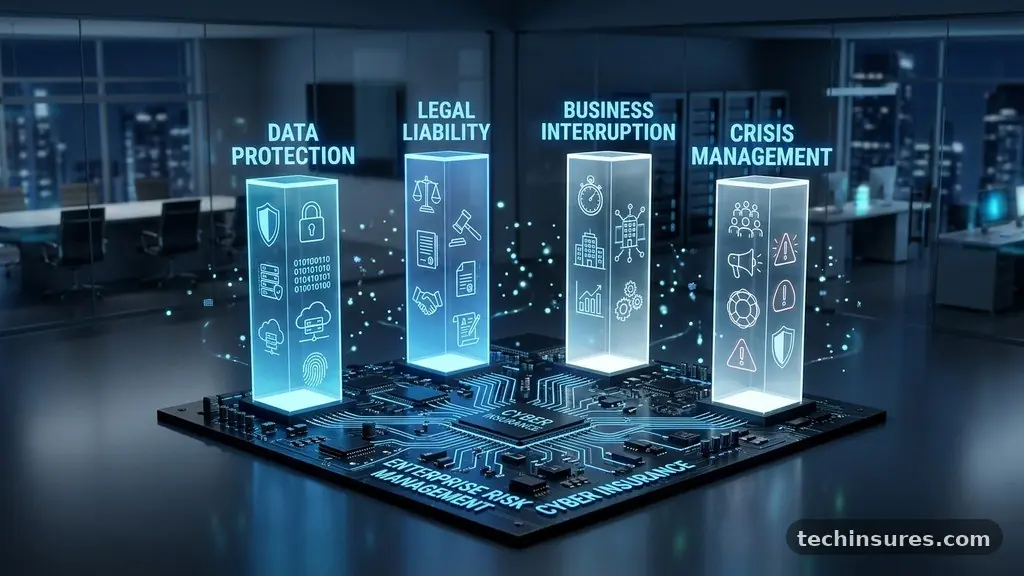
The Core Pillars of Cyber Coverage
At its heart, cyber insurance is designed to mitigate the financial impact of digital attacks and data breaches. When you look at cyber insurance explained: what does it actually cover the primary answer is the recovery phase following an incident.
This includes the immediate costs of forensic investigations to determine how a hacker gained entry. It also covers the legal expenses associated with defending your organization against lawsuits or regulatory fines.
Most policies act as a safety net for both first-party and third-party losses. First-party coverage deals with the costs you incur directly, such as the expense of notifying customers about a data breach. It also covers the costs of credit monitoring services for affected individuals and public relations efforts to repair your brand’s reputation.
Third-party coverage, meanwhile, focuses on your liability to others. If a client sues you because their sensitive information was exposed through your systems, this portion of the policy helps pay for legal fees and settlements.
Breaking Down Common Policy Exclusions
Knowing what is excluded is just as important as knowing what is covered. Most standard policies do not pay out for the loss of future profits or the devaluation of your company due to a tarnished reputation.
They also typically exclude costs associated with improving your IT infrastructure after a breach. If your systems were outdated, the insurance company will pay to restore them to their previous state, but they generally won’t pay to upgrade them to a more secure version.
Another common exclusion involves acts of war or state-sponsored cyber warfare. Because these events are so destructive and unpredictable, many insurers include language that limits their liability in these specific scenarios.
Furthermore, damage to physical property caused by a cyber event is often excluded unless you have a specific endorsement. If a hacker causes a server to overheat and catch fire, your cyber policy might not cover the hardware itself, even if it covers the data lost in the process.
Financial Protection Against Ransomware
Ransomware has become one of the most significant threats to modern organizations. When you have cyber insurance explained: what does it actually cover you will often find that ransom payments and negotiation fees are included, though this is heavily scrutinized.
Insurers frequently work with specialized crisis management firms to handle these negotiations on your behalf. They want to ensure that the payment actually leads to the decryption of your data rather than just emboldening the attackers.
Beyond the ransom payment itself, these policies cover the business interruption losses you suffer while your systems are offline. If your manufacturing line or e-commerce platform is down for a week, the lost revenue can be catastrophic.
Cyber insurance aims to replace that lost income during the period of restoration. This ensures that you can continue paying employees and meeting basic financial obligations while your IT team works to restore order.
Key Financial Components of Policies
| Coverage Category | What It Typically Includes |
|---|---|
| Data Recovery | Costs to restore, recreate, or recollect lost data. |
| Legal Liability | Defense costs and settlements for privacy lawsuits. |
| Business Interruption | Lost revenue while systems are non-operational. |
| Extortion Payments | Funds used to pay hackers for decryption keys. |
The Role of Forensic Investigation
When a breach occurs, the first step is almost always a forensic investigation. You need to know exactly what was taken and how the intruders got in.
Most high-quality cyber policies include a pre-approved list of forensic experts who can be deployed immediately. This is a critical benefit because speed is essential in minimizing the total impact of a breach.
These experts identify the entry point and ensure the threat has been fully eradicated. Without this, you might pay a ransom or restore a backup only to have the hackers re-enter the following day.
The insurance provider covers the hourly rates of these professionals, which can be quite substantial. By outsourcing this to experts, you avoid the common mistakes that occur when an internal team is overwhelmed or lacks specific incident response experience.
Regulatory Fines and Notification Costs
Data protection laws have become increasingly strict, with regulations like the GDPR and CCPA imposing heavy fines for mishandling sensitive information. If your organization is found to be in violation of these laws following a breach, your insurance may cover the cost of regulatory fines.
However, it is important to note that many jurisdictions prohibit the insurance of certain types of punitive damages. You should always check the specific language in your policy to see what is legally insurable in your operating region.
Notification requirements also represent a major hidden cost. If you lose the data of thousands of customers, you are legally required to inform them.
This process involves legal counsel, mailing services, and call center support to answer customer inquiries. These administrative costs add up very quickly, and they are almost always included under the “notification and crisis management” section of a standard policy.
The Importance of Ongoing Security
Insurance is not a replacement for strong cybersecurity practices. In fact, many insurance providers now require you to demonstrate specific security controls before they will even write a policy.
This often includes implementing multi-factor authentication, regular data backups, and employee training sessions. If you fail to maintain these standards, you might find that your claim is denied later.
Think of your security stack as the foundation and the insurance policy as the roof. You need both to keep the house dry during a storm.
If you have no security controls, your premiums will be prohibitively expensive, if you can get coverage at all. For more information on building a strong foundation, you can review the guidance provided by the Cybersecurity and Infrastructure Security Agency regarding best practices for business defense.
Common Security Requirements for Policyholders
- Mandatory multi-factor authentication for all remote access.
- Regular, encrypted, and off-site data backups.
- Endpoint detection and response software on all devices.
- Formal incident response plans that are tested annually.
- Regular security awareness training for all staff members.
The Claims Process Explained
Filing a claim is not as simple as calling your agent and sending an invoice. You must provide extensive documentation to prove the extent of the loss and the steps taken to mitigate it.
This is why having an incident response plan in place before an event occurs is so vital. When you are in the middle of a crisis, you will not want to be figuring out how to document your losses for the first time.
Insurers will look for evidence that you took reasonable steps to secure your network before the attack. They may request logs, system configurations, and proof of software updates.
If they find evidence of gross negligence, such as using default passwords on critical infrastructure, they may reduce or deny the payout. This highlights why cyber insurance is a partnership rather than a passive safety net.
Frequently Asked Questions
Does cyber insurance cover human error?
Yes, most policies include coverage for losses resulting from human error. This includes scenarios where an employee accidentally deletes critical data or falls for a phishing scam that leads to a breach.
Is the cost of upgrading software covered?
Generally, no. Insurance covers the cost to restore your systems to their previous state. It does not pay for improvements or upgrades intended to make your system better than it was before the incident.
Do I need cyber insurance if I use cloud services?
Yes, you still need it. Even if your data is stored in the cloud, you are still responsible for the security of your account and the data you upload. Cloud providers typically do not cover your liability if your specific credentials are compromised.
How are premiums determined?
Premiums are based on your industry, the amount of sensitive data you handle, your annual revenue, and your existing security controls. Companies with better security hygiene generally pay lower premiums.
Final Considerations
Navigating the world of digital protection requires a clear understanding of your specific risks. When you have cyber insurance explained: what does it actually cover you can see that it acts as a vital tool for business continuity rather than just a way to recoup losses. It provides the financial and technical resources to weather the storm of a cyberattack.
By combining this coverage with a proactive security posture, you protect your organization’s future. Take the time to audit your current policy, speak with your broker about potential gaps, and ensure your team is prepared to act when the unexpected happens. Your resilience depends on the preparations you make today.