How Businesses Can Protect Customer Data Online
Learning how businesses can protect customer data online is no longer an optional task for tech giants; it is a fundamental pillar of modern commerce. Whether you run a local storefront or a growing digital startup, your customers trust you with their most private details.
When you prioritize data security, you build long-term loyalty and avoid the devastating costs of a breach. This article provides a clear roadmap for securing your digital assets and maintaining the integrity of the information you manage every day.
The Core Pillars of Data Security
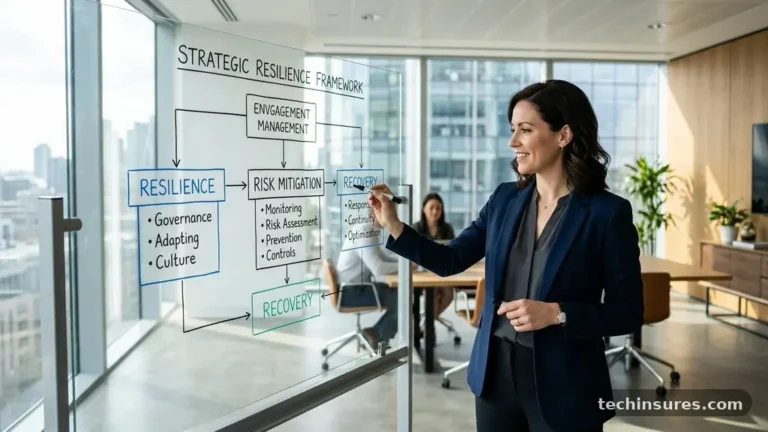
To understand how businesses can protect customer data online, you must first recognize that security is not a single tool but a multi-layered strategy. The most effective approach involves combining technical safeguards with consistent internal policies.
You cannot simply install software and walk away, as digital threats evolve constantly. Instead, think of your data protection strategy as an ongoing process of assessment and improvement.
Identifying Sensitive Information
You cannot defend what you haven’t identified. Start by creating a detailed inventory of the data you collect, store, and process. This includes names, email addresses, payment information, and IP addresses.
Categorize this information based on its sensitivity level. Publicly available business contact details require different handling than a customer’s social security number or credit card digits.
Implementing Encryption
Encryption acts as a digital lock for your data. Even if an unauthorized party manages to intercept your files, they will see only scrambled, unreadable code rather than clear personal details.
Ensure that all sensitive data is encrypted both while it is being transferred across the internet and while it is stored on your servers. Use standard protocols like AES-256 for storage and TLS for web traffic to ensure industry-standard protection.
Managing Access and Permissions
One of the most common ways data leaks occur is through simple human error or excessive access rights. You should follow the principle of least privilege, which dictates that employees only have access to the specific files and systems they need to perform their jobs. If a marketing intern does not need to see a customer’s full transaction history, that access should be blocked by default.
Enforcing Strong Authentication
Passwords are rarely enough to stop a determined attacker. Implementing multi-factor authentication (MFA) adds a vital layer of security by requiring a second form of verification, such as a code sent to a mobile device or a fingerprint scan.
This ensures that even if a password is compromised, the attacker still cannot breach the system. Make it a mandatory policy for everyone in your organization, regardless of their seniority level.
Reviewing User Rights Regularly
Permissions often creep upward over time as employees change roles or projects. Conduct a formal audit of user access rights every quarter to ensure they remain appropriate.
Remove access for former employees immediately upon their departure. These small, administrative tasks are often the most effective barriers against internal data mishandling or accidental exposure.
Training Staff on Security Awareness
Your employees are often the first line of defense for your digital infrastructure. Most security breaches stem from phishing attempts or social engineering tactics that target human psychology rather than technical flaws.
Regular training sessions help staff recognize these threats before they cause damage. A well-informed team is significantly less likely to click on a malicious link or share credentials.
Recognizing Phishing Attempts
Teach your team to scrutinize email senders, check for suspicious links, and verify requests for sensitive information. Phishing emails have become incredibly sophisticated, often mimicking the branding of trusted services or internal company communications. Encourage a culture where employees feel comfortable verifying unusual requests with the IT department rather than acting on them immediately.
Establishing Clear Security Protocols
Create a simple, accessible document that outlines your company’s data handling policies. This should cover everything from how to handle customer inquiries to the proper disposal of digital records.
When expectations are clearly documented, it removes ambiguity from daily operations. Use the following list to guide your baseline policy development:
- Require password updates every 90 days.
- Ban the use of personal devices for accessing company databases.
- Mandate the use of encrypted messaging tools for sensitive communications.
- Implement automatic screen locks on all office computers.
- Require VPN usage for any staff working from remote locations.
Securing Third-Party Vendor Relationships
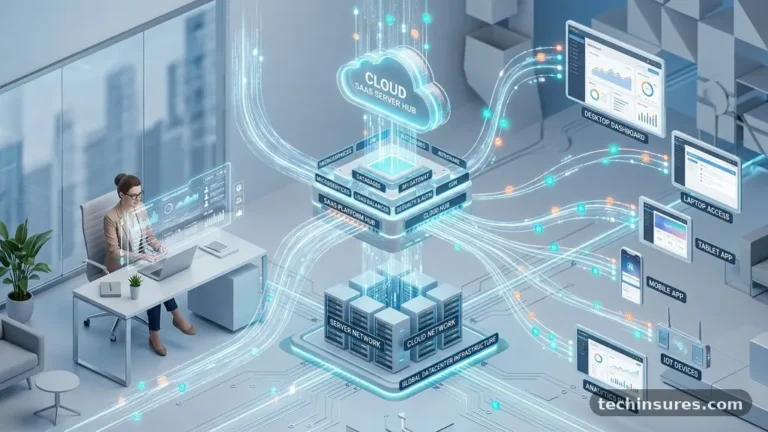
Modern companies rely on a web of software, cloud storage, and payment processors to function. While these tools make your operations more efficient, they also expand your attack surface.
You are responsible for the data you pass to these vendors, so you must ensure they meet your security standards. Before signing a contract, ask for proof of their security certifications and data handling practices.
Evaluating Vendor Security
Look for vendors that provide clear documentation regarding their data protection measures. If a provider cannot explain how they secure your customers’ information, they are likely not the right partner for your business. You can check for industry-standard certifications such as SOC 2 or ISO 27001 to gauge their level of commitment to security.
The Role of Data Contracts
Always include a data processing agreement in your contracts with third-party providers. This legal document should explicitly state how the vendor will protect the data, how they will notify you of a breach, and what their responsibilities are if a leak occurs. Never assume that a vendor is handling your data securely simply because they are a large, well-known company.
Comparing Security Measures for Small Businesses
Small businesses often operate with fewer resources than large corporations, but this does not mean they are exempt from security requirements. The goal is to choose cost-effective measures that provide maximum protection against the most common threats.
Many cloud-based services offer built-in security features that are perfectly adequate for smaller operations. The table below highlights common security tools and their primary benefits for growing teams.
| Security Tool | Primary Function | Benefit to Small Business |
|---|---|---|
| Hardware Firewall | Traffic filtering | Blocks unauthorized network access at the perimeter. |
| Password Manager | Credential security | Forces complex passwords and reduces reuse. |
| Cloud Backup | Data recovery | Protects against ransomware by keeping off-site copies. |
| Endpoint Protection | Device security | Monitors individual laptops for malware and viruses. |
Responding to a Data Breach
Even with the best precautions, accidents can happen. Having a formal incident response plan is critical to minimizing damage if a breach occurs.
Your plan should clearly define who is responsible for each step of the response, from identifying the source of the leak to notifying affected customers. Speed is essential, but accuracy in your communication is equally important.
Communicating with Customers
Transparency is the best policy when you have failed to protect customer data. Notify your clients promptly if their personal information has been accessed or stolen.
Provide them with specific instructions on what they should do next, such as changing passwords or monitoring their bank statements. A proactive, honest apology can help retain trust even after an unfortunate incident.
Technical Recovery Steps
Once you have contained the breach, your IT team must conduct a thorough forensic analysis to determine how the attackers gained access. Patch the vulnerability immediately and change all administrative credentials.
Document every step taken during the recovery process, as this will be necessary for regulatory compliance and insurance reporting. You can find further guidance on incident management at the Cybersecurity and Infrastructure Security Agency website.
Maintaining Long-Term Compliance
Data privacy regulations are becoming more stringent around the world. Laws like the GDPR in Europe or the CCPA in California dictate how companies must handle personal information.
Even if you are not currently operating in these regions, aligning your practices with these standards is a smart way to future-proof your business. These regulations are essentially a baseline for ethical data management.
Continuous Monitoring
Security is not a static goal. You must continuously monitor your systems for anomalies or suspicious patterns of activity.
Many automated tools can alert your team to failed login attempts or unusual data exports. By catching these signs early, you can stop a potential incident before it evolves into a full-scale catastrophe.
Updating Internal Policies
Review your security policies annually to ensure they reflect the latest technological advancements and threat landscapes. As your company grows, your data protection needs will change.
If you scale up your operations or start collecting new types of data, update your privacy policy and security protocols to match those new realities. Regular reviews keep security at the forefront of your company culture.
Frequently Asked Questions
How often should we change company passwords?
Most security experts recommend changing passwords every 90 days, or immediately if you suspect a compromise. However, the use of a password manager is more important than the frequency of changes, as it allows for long, complex, and unique passwords for every account.
What is the most common cause of data breaches?
Human error remains the leading cause of data breaches. This includes falling for phishing emails, using weak passwords, or misconfiguring cloud storage settings. Regular training and simple, automated security tools can significantly reduce these risks.
Do small businesses really need to worry about hackers?
Yes, small businesses are often targeted because they are perceived as having weaker security than large corporations. Attackers use automated bots to scan for vulnerabilities across the internet, meaning your business can be targeted even if you are not a specific or high-profile objective.
What should I do if my business is hit by ransomware?
Never pay the ransom, as there is no guarantee that you will regain access to your data or that it won’t be leaked anyway. Instead, isolate the affected systems, notify law enforcement, and restore your data from secure, offline backups.
How do I know if my third-party vendors are secure?
Ask for their latest security audit reports, such as a SOC 2 Type II report. If they cannot provide documentation of their security practices, consider it a red flag and look for providers that prioritize data privacy.
Conclusion
Protecting customer data is a continuous commitment to the people who keep your business running. By implementing strong encryption, managing user access, and training your staff, you create a culture of security that protects your reputation and your clients’ peace of mind. Remember that the goal is not to achieve perfection but to be resilient and prepared.
As you look at how businesses can protect customer data online, prioritize the steps that offer the highest impact, such as enabling multi-factor authentication and auditing your vendor agreements. Start today by reviewing your current access logs and ensuring your team understands the basics of phishing prevention.
By taking these proactive measures, you demonstrate that your company values its customers above all else. Consistent, small improvements to your security posture will pay dividends in trust and stability for years to come.