What Is Cloud Security and How Does It Protect Business Data?
Understanding cloud security and how does it protect business data is essential for any modern organization moving assets off-site. As companies migrate from physical servers to digital infrastructure, the perimeter of the network effectively dissolves, making traditional firewalls insufficient. Protecting information in these remote environments requires a shift in how teams manage access, encryption, and monitoring.
This article explores the mechanics of these defenses and why they are necessary for maintaining operational integrity in a digital-first economy. You will gain a clearer picture of the tools and strategies that keep private information safe from unauthorized parties.
Defining Cloud Security and Its Core Purpose
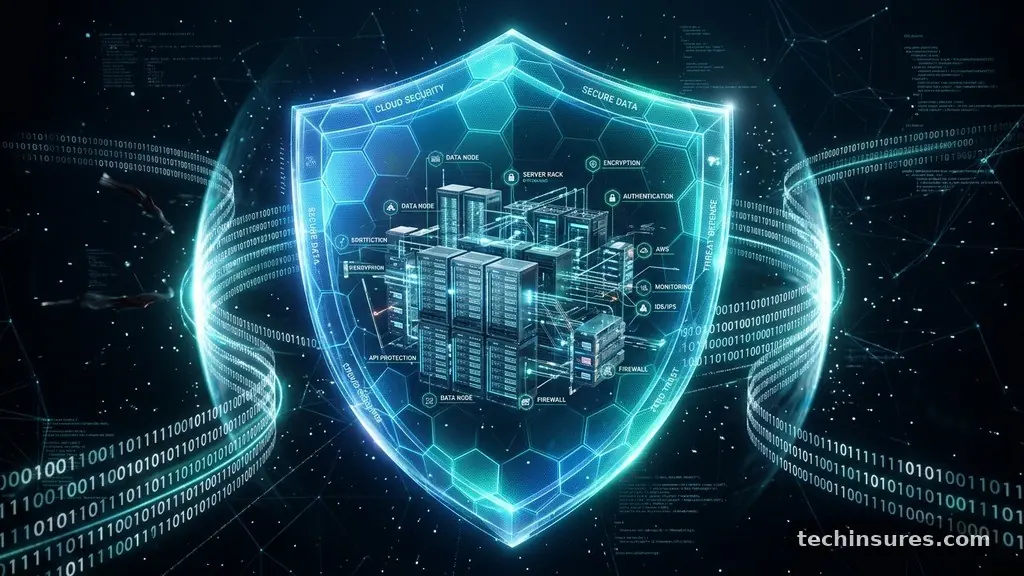
At its simplest level, cloud security refers to the collection of policies, technologies, and controls deployed to protect data, applications, and the associated infrastructure of cloud computing. When you ask what is cloud security and how does it protect business data, the answer lies in the shared responsibility model.
Cloud providers like Amazon Web Services or Microsoft Azure manage the security of the underlying hardware and global network. Meanwhile, the business remains responsible for securing the data they choose to store or process within those systems.
This security discipline acts as a digital vault that wraps around your files, whether they are sitting at rest in a server or moving across the internet. Without these layers, your information would be exposed to anyone who could guess a login credential or exploit a misconfigured setting.
The goal is not just to prevent theft but to ensure that your records remain accurate and accessible only to authorized personnel. By centralizing these controls, businesses can enforce strict rules that would be nearly impossible to manage across hundreds of individual office computers.
How Encryption Acts as a First Line of Defense
Encryption is perhaps the most critical technical component when discussing cloud security and how it protects business data. It works by transforming readable information into an unreadable format using a complex mathematical key.
Even if an attacker manages to intercept a data packet while it is being transmitted or gains unauthorized access to a physical storage drive, the information remains gibberish without the specific decryption key. This process effectively renders stolen data useless to criminals.
Most providers offer two distinct types of encryption that businesses must leverage to be truly safe. Data at rest is encrypted while sitting on a database or hard drive, protecting it from physical theft or unauthorized server access.
Data in transit is encrypted while moving between your local machine and the cloud, preventing eavesdropping on public or private networks. Modern standards like AES-256 are the industry benchmark for these operations, providing a level of complexity that is computationally infeasible to break with current hardware.
Managing Identity and Access for Better Control
Identity and Access Management, often abbreviated as IAM, is the gatekeeper of your digital ecosystem. It ensures that only the right people have access to the specific resources they need to do their jobs.
When you consider cloud security and how does it protect business data, IAM is the primary mechanism for preventing internal leaks and limiting the blast radius of a compromised account. By assigning granular permissions, you ensure that an intern does not have the same administrative power as a senior IT director.
Permissions create a hierarchy of access that prevents excessive permissions from becoming a security risk. If an account is breached, the attacker is limited by the scope of that specific user’s role rather than having free reign over the entire company database.
Multi-factor authentication is a vital piece of this puzzle, requiring a secondary code or biometric scan to verify identity. This simple step stops the vast majority of automated password-spraying attacks that plague businesses today.
Visibility Across Hybrid and Multi-Cloud Setups
One of the biggest challenges for modern enterprises is maintaining a clear view of where information resides. Data distributed across multiple platforms can easily become a blind spot for security teams.
Cloud security and how it protects business data depends heavily on observability tools that provide a single pane of glass for monitoring activity. These tools log every interaction, from file modifications to login attempts, creating an audit trail that is indispensable during a forensic investigation.
When you operate across hybrid environments—a mix of on-premise servers and public cloud services—the complexity increases significantly. You need a unified strategy that applies the same level of scrutiny to both environments.
Without this central oversight, vulnerabilities that attackers look for can hide in the gaps between your private and public infrastructure. Consistent monitoring helps catch anomalies, such as an employee downloading an unusual volume of files at 3 AM, which could signal a potential insider threat or a compromised account.
The Role of Shared Responsibility in Data Safety
The partnership between a client and a provider is the foundation of modern digital safety. You can learn more about these specific frameworks through the National Institute of Standards and Technology, which outlines the guidelines for securing information systems.
Because cloud providers operate at a massive scale, they invest billions into physical security, such as armed guards, biometric scanners, and redundant power grids. These are assets a single business could never afford to replicate on its own.
However, the customer must hold up their end of the bargain by configuring the software correctly. Many data breaches are caused by simple human error, such as leaving a cloud storage bucket open to the public internet.
It is the responsibility of the business to audit their configurations and ensure that encryption is enabled for every new project. When both sides follow these protocols, the resulting architecture is significantly more resilient than a traditional local network.
Common Risks and How Security Measures Mitigate Them
Businesses face a variety of threats, ranging from sophisticated ransomware campaigns to simple misconfigurations. Theft and corruption are the most immediate dangers, but accidental deletion or service outages also pose significant risks to business continuity. The following table illustrates how specific security controls address these common threats to help you understand the practical value of your investment.
| Security Control | Threat Addressed | Primary Benefit |
|---|---|---|
| Encryption | Data Theft | Data is unreadable if intercepted. |
| IAM / MFA | Unauthorized Access | Prevents login via stolen credentials. |
| Automated Backups | Data Corruption | Quick restoration after a disaster. |
| Log Monitoring | Malicious Activity | Early detection of suspicious behavior. |
Each of these controls serves a specific purpose in a larger strategy. By layering these defenses, you create a system where a failure in one area does not lead to a total collapse of your security posture. This defense-in-depth approach is the gold standard for organizations that handle sensitive financial or personal information.
Frequently Asked Questions
What is cloud security in simple words?
Cloud security is the set of rules, tools, and practices used to protect data and applications hosted on remote servers. It ensures that only authorized users can access your files and that the information remains private while being moved or stored.
What are the main risks if I ignore cloud security?
Ignoring these protections leaves your data vulnerable to hackers, accidental data leaks, and regulatory fines. Without proper controls, your proprietary information could be stolen, leading to significant financial loss and permanent damage to your company’s reputation.
How does encryption protect my business data?
Encryption turns your sensitive information into an unreadable code that can only be unlocked with a specific key. Even if a criminal gains access to your files, they cannot read or use the information, effectively neutralizing the threat of a data breach.
What is the shared responsibility model?
This model defines who is responsible for what in a cloud environment. The cloud provider secures the physical hardware and infrastructure, while you are responsible for securing the data, access permissions, and configurations within your account.
Do small businesses really need advanced cloud security?
Yes, small businesses are often targeted because they are perceived as having weaker defenses. Implementing basic measures like multi-factor authentication and regular access audits is a low-cost, high-impact way to prevent the most common types of digital attacks.
Establishing a Secure Future for Your Data
Protecting your information is an ongoing process that requires constant vigilance rather than a one-time setup. As you continue to build your digital presence, remember that cloud security and how it protects business data is fundamentally about managing risk through layers of technology and policy. By prioritizing strong access controls, consistent encryption, and regular monitoring, you can create an environment where your team can collaborate safely from anywhere in the world.
Start by reviewing your current permissions and ensuring that multi-factor authentication is active for every user in your organization. If you need assistance with specific configurations, reach out to your cloud provider’s support team or a qualified security consultant to ensure your setup meets current industry standards. Your proactive efforts today will form the bedrock of your company’s long-term digital resilience.