What Is Zero Trust Security and Why Does It Matter?
Zero trust security is a strategic approach to cybersecurity that operates on the core principle of “never trust, always verify.” In an era where digital perimeters have dissolved, organizations must move away from the outdated idea that everything inside a corporate network is safe.
Understanding zero trust security and why does it matter involves recognizing that threats can originate from anywhere, including internal accounts or compromised devices. By implementing strict identity verification for every person and machine attempting to access resources, businesses can significantly reduce their exposure to modern data breaches.
Core Principles of the Zero Trust Model
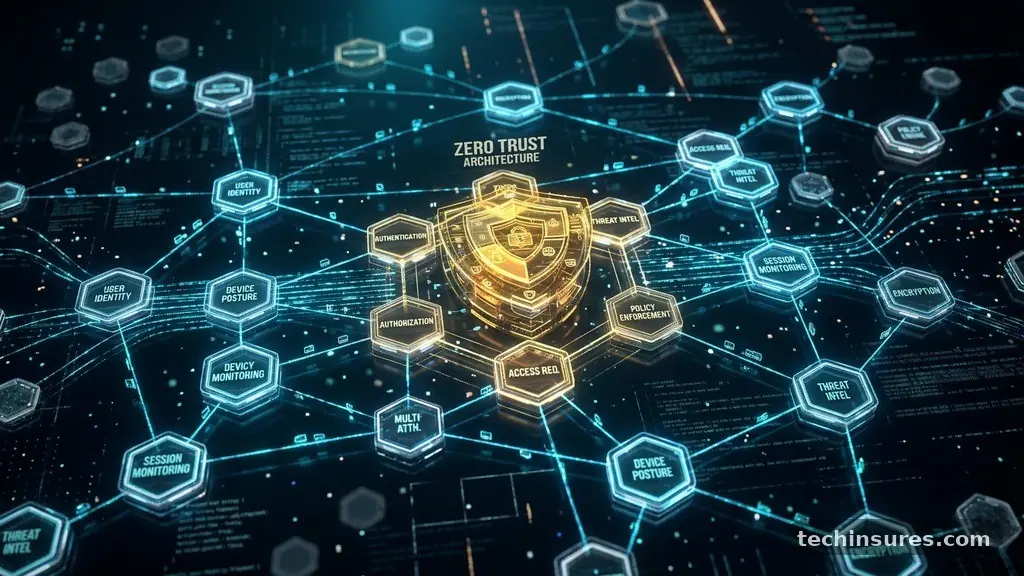
At its heart, the zero trust architecture rests on three fundamental pillars that define how information is protected. First, every access request must be fully authenticated, authorized, and encrypted before being granted. This means that simply being on the office Wi-Fi or behind a firewall is no longer sufficient to gain entry to sensitive applications.
Second, the system adheres to the principle of least privilege. Users are granted only the minimum level of access required to perform their specific job functions, and nothing more.
If a marketing coordinator does not need access to the engineering source code, the system denies that request by default. This limits the “blast radius” if a single user account becomes compromised.
Third, the model assumes that a breach is inevitable or has already occurred. Instead of focusing solely on keeping attackers out, the framework emphasizes continuous monitoring and validation. This proactive stance ensures that if an unauthorized entity gains a foothold, they cannot move laterally across the network to reach high-value targets.
Why Traditional Perimeter Security Fails
For decades, cybersecurity relied on the “castle-and-moat” strategy. IT teams built strong firewalls to protect the perimeter, assuming that anyone inside that perimeter was a trusted entity. While this worked in the era of on-premises servers, the modern digital landscape has fundamentally changed.
Cloud computing, remote work, and mobile devices have effectively obliterated the traditional network edge. Employees now access company data from coffee shops, home offices, and public transit, often using personal laptops or smartphones. When the network is everywhere, the concept of a single protected perimeter becomes obsolete.
Furthermore, attackers have become experts at bypassing traditional defenses through social engineering and stolen credentials. Once an attacker gains valid credentials, they can wander through a flat network undetected. Zero trust security and why does it matter becomes clear when you realize that identity—not location—is the new perimeter.
The Role of Identity and Access Management
Identity is the foundation of a modern security strategy. In a zero trust environment, the system must verify the identity of every user and device every single time they request access. This involves more than just a simple username and password, which are easily stolen or phished.
Most organizations now use multi-factor authentication (MFA) as a baseline requirement. Beyond simple passwords, the system analyzes contextual signals to determine if an access request is legitimate. These signals include the user’s location, the time of day, the health of the device, and the sensitivity of the data being requested.
If a user tries to log in from a new country at 3:00 AM using an outdated operating system, the system can trigger an additional verification step or block the request entirely. This granular level of control ensures that only authorized individuals can interact with sensitive business assets. You can learn more about these standards through the CISA Zero Trust Maturity Model, which provides a framework for federal agencies and private companies to assess their security posture.
Comparing Traditional Security to Zero Trust
Transitioning to a new security paradigm requires understanding the shift in philosophy. The following table highlights the key differences between the legacy approach and the modern, verification-focused strategy.
| Feature | Traditional Perimeter Model | Zero Trust Model |
|---|---|---|
| Trust Level | Implicit trust based on network location | Zero implicit trust; verify every request |
| Access Control | Broad access once inside the firewall | Granular, least-privilege access |
| Verification | One-time login at the perimeter | Continuous, real-time authentication |
| Network Design | Flat network structure | Micro-segmented network |
Key Components for Implementation
Implementing this architecture is a journey rather than a single software purchase. Organizations typically start by identifying their most critical data and applications—often called the “protect surface.” Once these assets are mapped, security teams can apply policies that restrict access to only those who absolutely need it.
Micro-segmentation is another critical technical component. By breaking the network into small, isolated zones, security professionals can prevent an attacker from moving from a low-security area to a high-security database. Each segment has its own security controls, making it difficult for threats to spread.
Visibility is equally important in this process. Without deep insights into network traffic and user behavior, it is impossible to verify requests effectively. Organizations must deploy tools that provide real-time analytics to spot anomalies, such as a sudden spike in data downloads or unusual login patterns.
Common Challenges and Considerations
Moving to a zero-trust model is rarely easy, especially for large organizations with legacy infrastructure. Many companies struggle with the sheer complexity of mapping every user, device, and application across the enterprise. It requires a significant cultural shift, as IT teams must move away from the convenience of open network access.
User experience is a frequent concern during the transition. If authentication processes are too cumbersome, employees may find ways to bypass security measures, which defeats the purpose of the program. Balancing robust security with a smooth, efficient workflow is the primary goal for any successful deployment.
* Legacy Application Incompatibility: Older software may not support modern authentication protocols.
* Data Silos: Different departments often use their own tools, making unified policy enforcement difficult.
* Cultural Resistance: Employees may view frequent verification as a sign of distrust or a productivity hurdle.
* Visibility Gaps: Incomplete logging and monitoring can leave blind spots in the security fabric.
Why This Matters for Future Resilience
The threat landscape is evolving faster than ever before. Ransomware attacks, supply chain vulnerabilities, and sophisticated phishing campaigns are now daily risks for businesses of all sizes. Relying on outdated defensive measures leaves organizations vulnerable to catastrophic financial and reputational damage.
Zero trust security and why does it matter comes down to business continuity and trust. Customers trust companies to keep their personal information safe. If a business fails to protect that data, it loses more than just money—it loses the confidence of its user base.
By adopting this model, organizations demonstrate a commitment to data integrity and privacy. It transforms security from a “cost of doing business” into a competitive advantage. Companies that can prove they have a mature, proactive security posture are more attractive to partners and clients alike.
Frequently Asked Questions
Is zero trust just about software?
No, it is a comprehensive strategy that combines technology, business processes, and organizational culture. While software tools like identity providers and micro-segmentation gateways are essential, they are only effective when guided by clear security policies and a “verify everything” mindset.
Does zero trust make the user experience worse?
It can if implemented poorly, but modern solutions aim to make security invisible. By using single sign-on (SSO) and adaptive authentication, users often have a smoother experience because they don’t have to manage dozens of different passwords for every application they use.
What happens if the network goes down?
This is a common concern, but modern zero trust solutions are designed with high availability in mind. Because authentication is distributed across cloud-based identity services, the failure of a single local server does not necessarily lock users out of their essential tools.
Can small businesses afford this approach?
Absolutely, as many cloud-based security platforms offer scalable pricing models for smaller teams. You don’t need a massive enterprise budget to start; you can begin by securing your most sensitive cloud applications and working outward from there.
Is it really possible to never trust?
The term “zero trust” is a philosophy of verification, not a state of paranoia. It means that trust is never granted based on where you are or what device you use, but is instead earned through constant, provable validation of your identity and security posture.
Final Thoughts
The transition toward a zero-trust architecture is no longer optional for organizations that take cybersecurity seriously. As digital threats grow in complexity, the old methods of relying on firewalls and physical office locations have become relics of a simpler time. Understanding zero trust security and why does it matter allows leadership teams to prioritize the protection of their most valuable data assets through rigorous identity verification and continuous monitoring.
Starting this journey involves assessing your current environment and identifying the most critical areas to protect first. You do not need to overhaul your entire infrastructure overnight to see the benefits.
Begin by implementing strong identity management and moving toward a least-privilege access model. By taking these incremental steps, you can significantly enhance your resilience against modern cyber threats and build a foundation for long-term success.